Idempotency ledger: stop AI agents double-charging
Fire 120 side-effect calls for 100 orders, and a naive runtime overcharges customers by $399.80. This isn't a glitch; it's the default behavior of standard retry mechanisms that mistake semantic decisions for network events. To achieve at-most-once safety, you need an idempotency ledger. This ledger distinguishes between lost requests and lost responses, stopping agents from double-charging when transport layers drop acknowledgments.
Exponential backoff and jitter won't save you here. Those tools only schedule retries; they don't verify if an action already happened. When a response vanishes, your agent can't tell if the request never arrived or if the money moved but the "ok" signal got lost. While providers like Stripe handle their own keys, your internal tools need a dedicated dedup key mapped to a recorded result to ensure deterministic execution.
The stakes are high. 81% of organizations with mature governance frameworks have rolled back customer-facing AI agents. 74% of enterprises have already shut down agents due to deployment failures. These aren't just outages; they are architectural flaws where "request succeeded, response lost" scenarios trigger duplicate writes. You need step-by-step implementation strategies to replace dangerous write retries with safe, ledger-backed operations.
The Mechanics of Response Loss and Double Charging
Response Loss Mechanics and the Semantic Retry Trap
Response loss hits when the transport layer discards an acknowledgment after a side effect, like a card charge, has already executed. Your agent calls a tool to charge a card. The response vanishes. Retry logic assumes failure and attempts the action again. A second charge hits the customer statement. This failure mode is a subset of network errors that standard retry logic mishandles without idempotency keys.
A retry isn't just a network event; it's a semantic decision about a side effect that may have already occurred. Standard at-least-once delivery guarantees ensure the request arrives but permit duplicate executions when responses vanish. Tuning backoff parameters without an at-most-once guarantee just makes the system double-charge on a slower, more polite schedule.
You must simulate network interruptions to verify agents don't duplicate side effects during repetitive prompts. The challenge is distinguishing request loss from response loss; since both look like timeouts, the system must assume the worst-case scenario where the remote mutation succeeded. Treat every write tool call as potentially committed until proven otherwise via deduplication keys.
Achieving At-Most-Once Behavior with Idempotency Ledgers
An idempotency ledger maps a deduplication key to a recorded result, ensuring side effects execute precisely once even when retries occur. This mechanism enforces at-most-once behavior by intercepting repeat requests and replaying the original response instead of re-triggering the underlying action. Traditional retry logic often resubmits tasks after client timeouts, causing side effects to execute once per instance; in contrast, durable agent architectures inspect receipts or idempotency keys before doing anything again, preventing re-execution traditional retry logic.
The operational necessity is acute. Data indicates that 74% of enterprises have rolled back or shut down a customer-facing AI agent after deployment, with the rate climbing to 81% among organizations with the most mature governance frameworks. These failures frequently stem from the "request succeeded, response lost" mode, identified as the primary driver for duplicate writes that standard retry logic mishandles without specific keys.
| Feature | Naive Retry Loop | Idempotency Ledger |
|---|---|---|
| Delivery Guarantee | At-least-once | At-most-once |
| Duplicate Risk | High (repeat side effects) | None (keyed replay) |
| Failure Handling | Assumes total failure | Distinguishes partial failure |
External systems create bottlenecks. If a payment provider processes a charge before the network drops the response, a local ledger cannot undo the transaction; the deduplication key must be validated by the provider's API to prevent the second charge. Consequently, autonomous agent workflows face a bottleneck in ensuring exactly-once processing, marking 2026 as a turning point for enterprise adoption of idempotent patterns critical bottleneck. You must integrate provider-specific keys rather than relying solely on internal state tracking.
At-Least-Once Versus At-Most-Once Delivery
At-least-once delivery executes actions one or more times: acceptable for reads, ruinous for monetary transactions where naive retry loops ignore lost responses. At-most-once delivery ensures an action runs zero or one time, preventing double billing even if the network drops the acknowledgment.
| Feature | At-Least-Once | At-Most-Once |
|---|---|---|
| Execution Count | ≥ 1 times | ≤ 1 time |
| Primary Risk | Duplicate writes | Lost updates |
| Suitable For | Idempotent reads | Financial charges |
| Retry Behavior | Re-executes blindly | Checks state first |
Ignoring this distinction costs money. Direct monetary loss from duplicate charges in financial operations is the result monetary loss. Backoff makes retries polite, yet it cannot distinguish between a lost request and a lost response. You must implement logical uniqueness checks before executing side effects. Achieving this safety requires external state coordination, adding latency to every transaction path. Without an idempotency ledger or provider-side keys, the system remains vulnerable to silent data corruption during standard network partitions.
Architecting At-Most-Once Safety with Idempotency Ledgers
The Three Moves of the call_once Function
Three atomic moves define the call_once function and stop duplicate charges dead. First, derive a stable key from the workflow ID and arguments so random UUIDs or shifting timestamps do not corrupt the hash. A varying key blinds the ledger to duplicate requests instantly. Second, look before leaping by querying the store; finding an existing key means returning the cached result without touching the external API. This inspection blocks re-execution even when the network swallows acknowledgments. Third, record before the response can be lost, writing the result immediately after the side effect fires but before the agent receives confirmation.
| Step | Action | Failure if Skipped |
|---|---|---|
| 1 | Derive stable key | Keys mismatch on retry |
| 2 | Check existence | Double charge occurs |
| 3 | Record result | Data loss on crash |
This sequence ensures that a ledger-backed runtime charging $19.99 per order executes exactly 100 calls, resulting in a balance of $1,999.00 rather than the inflated $2,398.80 seen in unmanaged loops. The critical insight demands that the write to the ledger and the external side effect occur in a single transaction; a crash between the charge and the log creates permanent inconsistency otherwise. Developers simulate these interruptions to verify backend state consistency across retry loops, a practice validated by industry evaluations of AI-driven state management AI solution for idempotency. Agents cannot distinguish a lost request from a lost response, triggering unnecessary retries that double-charge customers. Financial discrepancies like this show why standard backoff policies fail to protect write operations. Storing output against a deterministic key lets the system return the cached response on retry, ensuring the external API receives exactly one request. This approach aligns with emerging standards for simulation-based testing where developers validate agent behavior under simulated network interruptions.
Implement a local idempotency ledger whenever a tool call triggers an irreversible external state change. If the side effect is monetary or communicative, retry logic must consult local state before transmitting data. Relying solely on network timeouts creates a false sense of safety while exposing the system to semantic duplication. Added latency from a local database write is the cost; unbounded financial liability is the alternative. Without this guardrail, at-most-once safety remains impossible to guarantee in unstable network conditions.
Step-by-Step Implementation of an Idempotency Ledger
Deriving Stable Keys from Workflow ID and Step Arguments
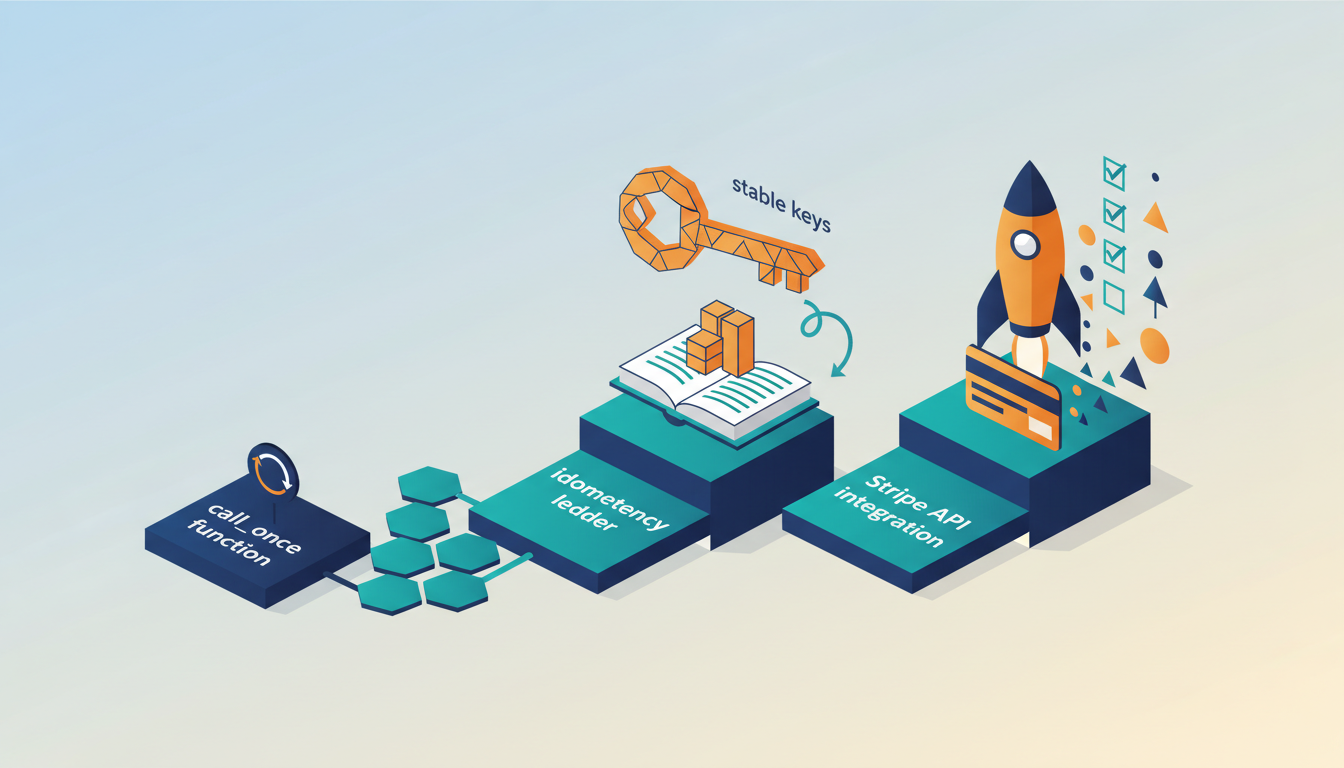
Generate a deterministic key from the workflow ID, step index, and action arguments to stop duplicate charges dead. This stable key acts as a unique fingerprint for the specific operation, mapping retries referencing the same logical intent to the original execution record. Incorporating timestamps or random UUIDs at call time breaks the idempotency ledger, allowing the side effect to fire again despite the retry.
- Concatenate the immutable workflow run ID, the integer step index, and the canonicalized action type.
- Hash the resulting string using SHA-256 to produce a fixed-length identifier.
- Store this identifier as the primary lookup key before invoking any external tool.
Think of this rigor as a circuit breaker for duplication, halting the system before it steps on its own toes during network partitions. A sharp limitation emerges if the model layer alters arguments slightly between attempts; the derived key shifts, and the ledger perceives a new request rather than a retry. Pin arguments at the call site to guarantee the hash remains consistent across all transmission attempts. Strict determinism is the only shield against double-spending.
Integrating Stripe Idempotency Keys via the Idempotency-Key Header
Pinning deterministic keys at the call site prevents the response loss failure mode where a charge succeeds but the acknowledgment never reaches the agent.
- Generate the idempotency key using only immutable workflow parameters before the model alters any arguments.
- Pass this exact string to Stripe via the
Idempotency-Keyheader in the initial HTTP request. - Rely on the provider to return the cached result for any subsequent request bearing the same key.
Standard retry logic often resubmits tasks after client timeouts, causing side effects to execute once per instance; durable agent architectures inspect receipts or idempotency keys before doing anything again, preventing re-execution Failure Handling Architecture. If the derivation logic incorporates timestamps or random UUIDs generated at call time, the system fails to ensure determinism on retry, rendering the safety mechanism useless. The architectural constraint is clear: the agent must trust the external provider's ledger rather than maintaining its own state for third-party actions. AI Agents News recommends this approach for any tool with irreversible financial consequences.
Ordering the Charge and the Ledger Write
A crash between the side effect firing and the record committing leaves the ledger blind to the duplicate on the next attempt. Workers must call a TryStart function against an idempotency store before executing any task, enforcing a strict ordering of operations that prioritizes state persistence over response delivery.
- Initiate the side effect call with the external provider using a pinned, deterministic key.
- Wait for the provider's acknowledgment containing the final status and payload.
- Write the result to the local idempotency ledger within the same database transaction as the workflow state update.
- Return the cached result to the agent only after the local commit confirms success.
Multi-tiered strategies expand this definition to include logical uniqueness across layers, ensuring side-effect protection even if the upstream workflow restarts unaware of the prior completion. Local ledgers cannot fully protect against crashes unless the provider also supports idempotent keys; otherwise, the remote system will accept the retry regardless of local state. Tag calls to critical financial tools and require manual confirmation if the provider lacks native deduplication headers. AI Agents News recommends pinning deterministic keys at the call site to ensure the model cannot alter arguments before the key is generated.
Validating Financial Integrity Through Simulation and Risk Analysis
Defining the Atomic Commit Requirement for Ledgers
Crashes expose the gap between a ledger record and an external side effect when these events fail to finalize as one indivisible unit. Separation invites disaster if the system fails after charging a card but before writing the local log. Restarted agents see no history and safely retry the payment, unknowingly initiating a second charge. Parallel retries bypass detection logic entirely without atomic check-and-record operations like INSERT... ON CONFLICT DO NOTHING in Postgres. This specific gap turns a standard network timeout into a direct financial liability because the agent cannot distinguish a lost request from a lost response. Literature identifies financial operations as a domain where agents must verify incomplete logs on restart to decide between rolling back or proceeding, rather than blindly re-executing financial operations. Any implementation separating the mutation from its receipt fails the at-most-once guarantee required for production finance tools. Treat the write and the log as one physical operation, or the system remains vulnerable to duplicate execution regardless of key stability.
Simulating Cost Savings: Naive Retry vs Ledger Runtime
Network interruption simulations show naive retry loops executing 120 side-effect calls for just 100 orders. Duplicate charges inflate costs by 20 percent. Standard backoff mechanisms treat response loss as a request failure, forcing the agent to re-execute the transaction blindly. Developers now employ Simulation-Based Testing to validate that backend state remains consistent when transport layers drop acknowledgments. A ledger-based runtime prevents this erosion by deriving a stable key from workflow parameters before any external call occurs. The system returns the cached result instead of firing the tool again if the key exists in the store.
Critical Failure Modes: Non-Deterministic Keys and False Deduplication
Regenerating LLM arguments on retry alters the idempotency key, causing the ledger to miss duplicates entirely. Fresh tokens or reformatted JSON during a retry attempt change the derived hash, so the system treats a repeated financial transaction as a new request. This non-deterministic behavior breaks the at-most-once guarantee because the lookup fails to find the original successful charge recorded upstream. Keys constructed from coarse data like item SKUs alone trigger false deduplication, where distinct, legitimate orders are incorrectly blocked as duplicates. Operational tension lies between key stability and argument flexibility; builders must pin deterministic inputs before the model generates any variable content. If the key generation includes timestamps or random UUIDs, the durable agent architectures cannot inspect receipts effectively to prevent re-execution. Relying on immutable factors like workflow run IDs is mandatory, as using values generated at call time explicitly breaks determinism required for production workflow safety. Ignoring this specificity causes measurable financial leakage rather than simple data inconsistency. Network operators must enforce strict schema validation on key inputs so the ledger remains the single source of truth for transaction state. The retry mechanism increases errors rather than recovering from them without this discipline.
About
Diego Alvarez is a Developer Advocate at AI Agents News, where he specializes in building and benchmarking autonomous agent frameworks like CrewAI and LangGraph. His daily work involves constructing end-to-end agentic systems, giving him direct experience with the precise failure modes discussed in this article. When engineering agents that execute financial transactions, Alvarez frequently encounters the critical gap between network retries and actual side effects. This practical exposure makes him uniquely qualified to explain why standard retry logic fails when an idempotency ledger is absent. At AI Agents News, the team focuses on providing engineers with reliable, production-grade insights rather than hype. By connecting the theoretical concept of an idempotency ledger to real-world tool-calling scenarios, Alvarez bridges the gap between abstract distributed systems theory and the concrete challenges of preventing double-charges in live deployments.
Conclusion
Scaling financial transactions exposes a brutal reality where infrastructure instability transforms naive retry logic into active revenue leakage. The operational cost here is not merely technical debt but direct financial liability, as non-deterministic keys cause systems to charge customers multiple times for single intents. You cannot rely on standard application logic to fix this because the failure mode exists specifically when the network fails and the system attempts recovery. The solution demands a shift toward atomic check-and-record operations that enforce strict determinism before any model generation occurs.
Organizations must mandate that idempotency keys derive solely from immutable workflow inputs rather than flexible runtime values. This architectural constraint is the only way to guarantee that a ledger acts as a true single source of truth rather than a passive log of errors.
Start this week by auditing your current key generation functions to ensure they exclude timestamps, random UUIDs, or LLM-generated content before they reach the database layer. Implementing this validation now prevents the compounding errors that arise when distributed systems interact with stateful financial records under pressure.
Frequently Asked Questions
A naive runtime overcharges customers by $399.80 when firing 120 calls for 100 orders. Implementing a ledger ensures exactly 100 executions, reducing errors to $0.00 and preventing financial leakage from lost responses.
Standard retries treat semantic decisions as network events, causing double charges when responses are lost. This flaw drives 81% of mature organizations to roll back agents, necessitating ledgers that distinguish request loss from response loss.
Data shows 74% of enterprises have rolled back customer-facing agents after deployment failures. These outages often stem from duplicate writes, requiring architects to replace naive loops with idempotency ledgers for at-most-once safety.
The ledger maps a deduplication key to a recorded result, replaying the original response instead of re-charging. This prevents the inflated $2,398.80 balance seen in unmanaged loops, ensuring the balance remains $1,999.00.
A naive loop charging $19.99 per order creates a $399.80 error on 100 orders. An idempotent ledger fires exactly 100 times, resulting in a perfect $0.00 error rate despite identical network conditions.
References